$4.99M
Reduce breach exposure.
With an average of around USD 4.99M per breach, ranking top risks by business impact helps focus on what could prevent one.
Understand your real security posture and get a clear, prioritized roadmap to close the gaps that matter most
Most organizations don’t know where their real security exposure lies until it’s tested.
Our Security Assessment & Advisory service benchmarks your current posture against industry frameworks and attacker techniques, then translates the findings into a prioritized, business-aligned roadmap, so leadership can make informed decisions.
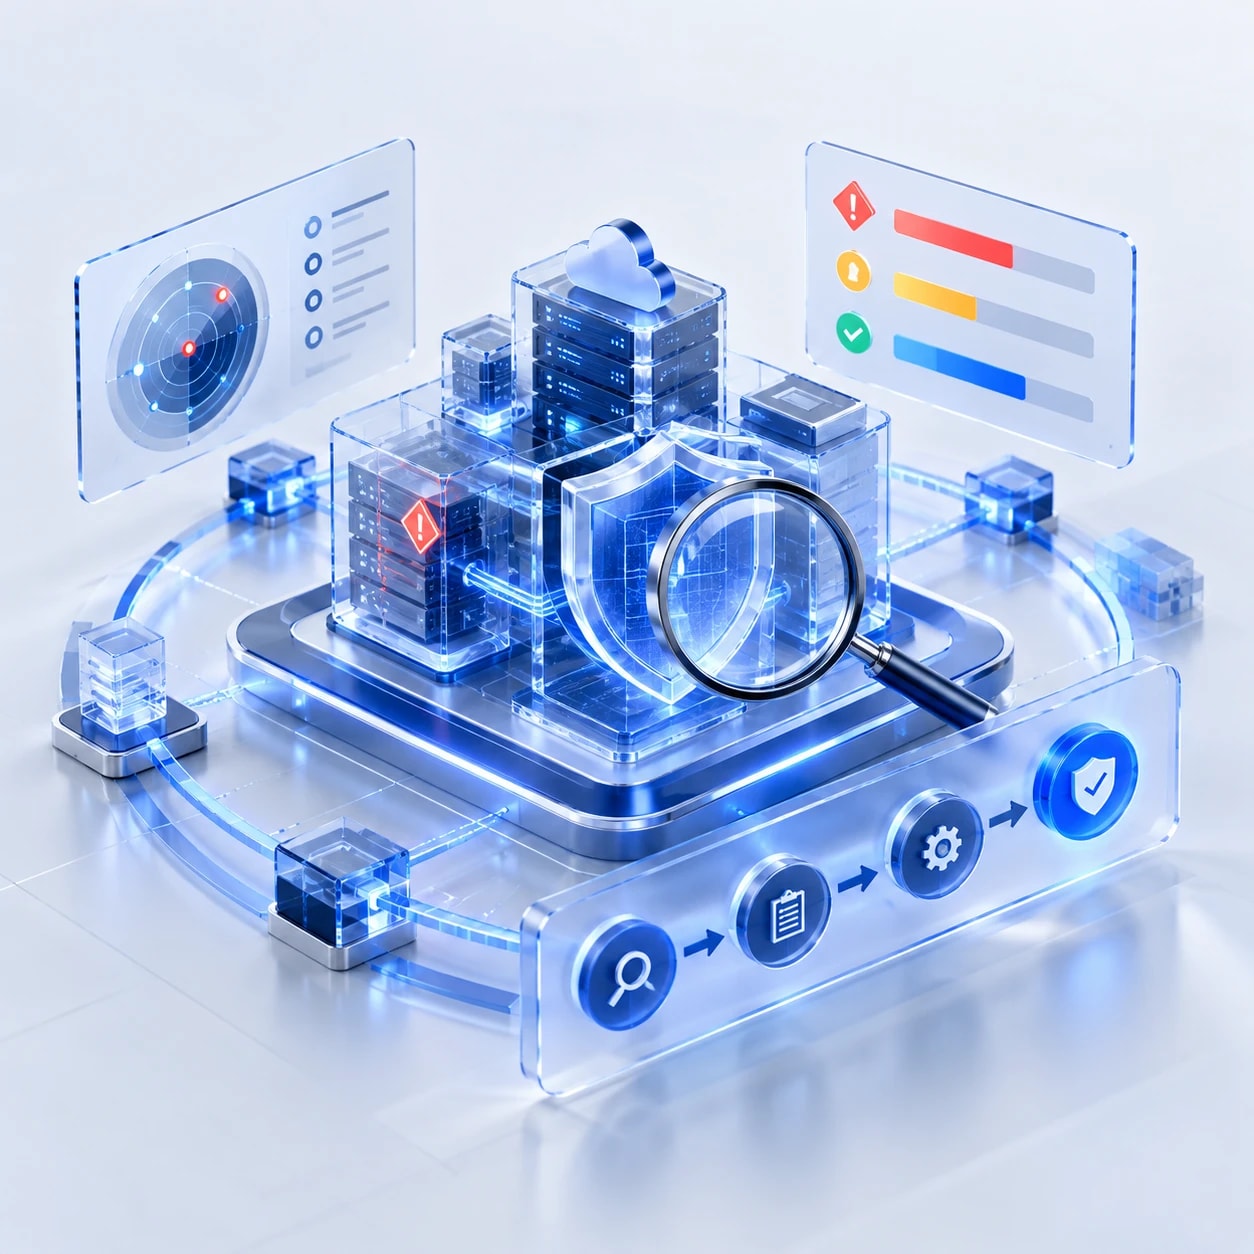

Translate technical findings into a prioritized business decision, audit evidence and a clear next move.
With an average of around USD 4.99M per breach, ranking top risks by business impact helps focus on what could prevent one.
Documented control maturity strengthens audit and insurance readiness.
Leadership gets an executive-ready risk register and roadmap for faster, better-informed security decisions.
An evidence-based assessment that moves from control review to tested exposure and a clear remediation plan.

A review of your policies, architecture and controls against NIST CSF and ISO 27001.

Testing across your network, application and cloud environments.

A risk register and an executive-ready remediation roadmap.
3–6 weeks, depending on scope.
Security Lead, Penetration Tester and Risk Analyst.
NIST CSF, ISO 27001, MITRE ATT&CK, Nessus, Burp Suite and Kali Linux.
Delivered in-house.
A fixed fee per assessment. Contact us for a quote.
Access to relevant systems and documentation, a stakeholder for interviews, and an agreed testing window.
Start with a 3–6 week assessment and find your real exposure before attackers do.