$6M
Prevent costly attacks.
Around USD 6M in losses can be prevented from model inversion, with reduced risk of model theft, manipulation or data leakage.
Protect your AI systems from the threats generic security programs miss
AI and ML systems introduce risks that traditional security programs aren’t built to catch, including model theft, data poisoning, prompt injection and adversarial inputs.
Our AI & ML Security service assesses and secures your models, pipelines and data across the AI lifecycle, so you can deploy AI with confidence rather than exposure.
AI-specific controls reduce exposure while giving regulators, customers and delivery teams clear assurance.
Around USD 6M in losses can be prevented from model inversion, with reduced risk of model theft, manipulation or data leakage.
You get a documented AI risk posture for regulatory and customer assurance.
Security becomes an enabler for safer, faster AI adoption across the business.
Focused protection across the model, data and operational pipeline.

A risk review of your models, pipelines and training data.

Simulation of prompt injection, data poisoning and model evasion.
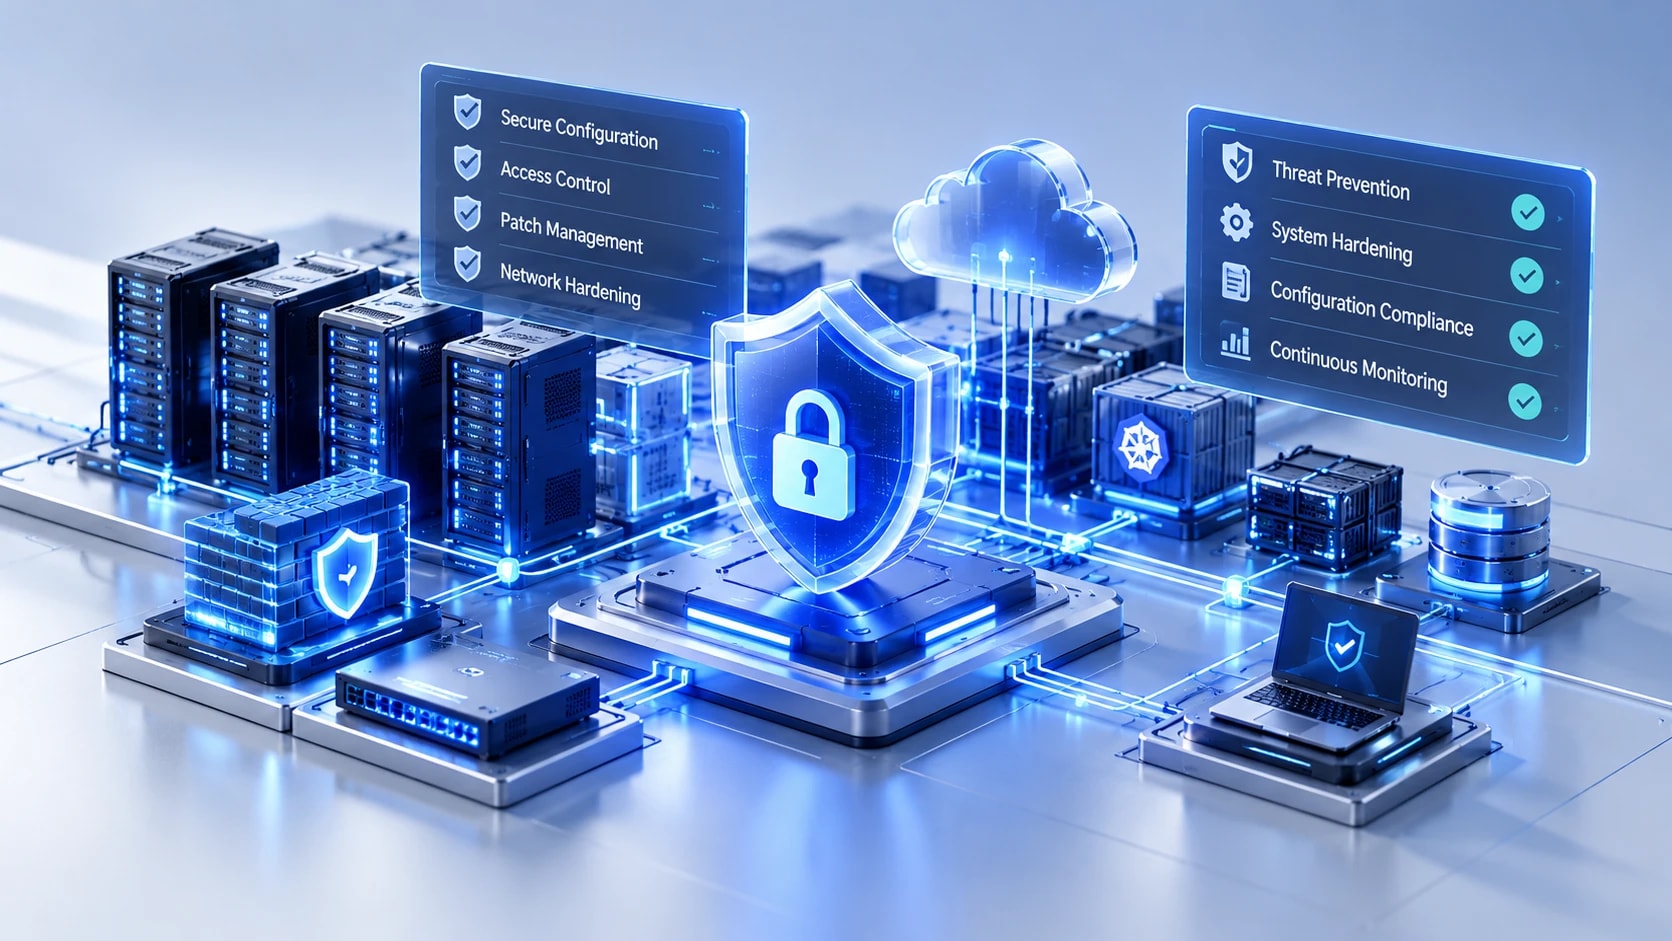
Access control, model versioning and monitoring for your AI pipelines.
4–8 weeks, depending on model complexity.
AI Security Lead, ML Engineer and Data Security Analyst.
MITRE ATLAS, OWASP ML Top 10, and model-scanning and LLM red-teaming tooling.
Delivered in-house.
A fixed fee per assessment. Contact us for a quote.
Access to models and pipelines (or a representative sandbox), training-data documentation, and an AI/ML architecture SME.
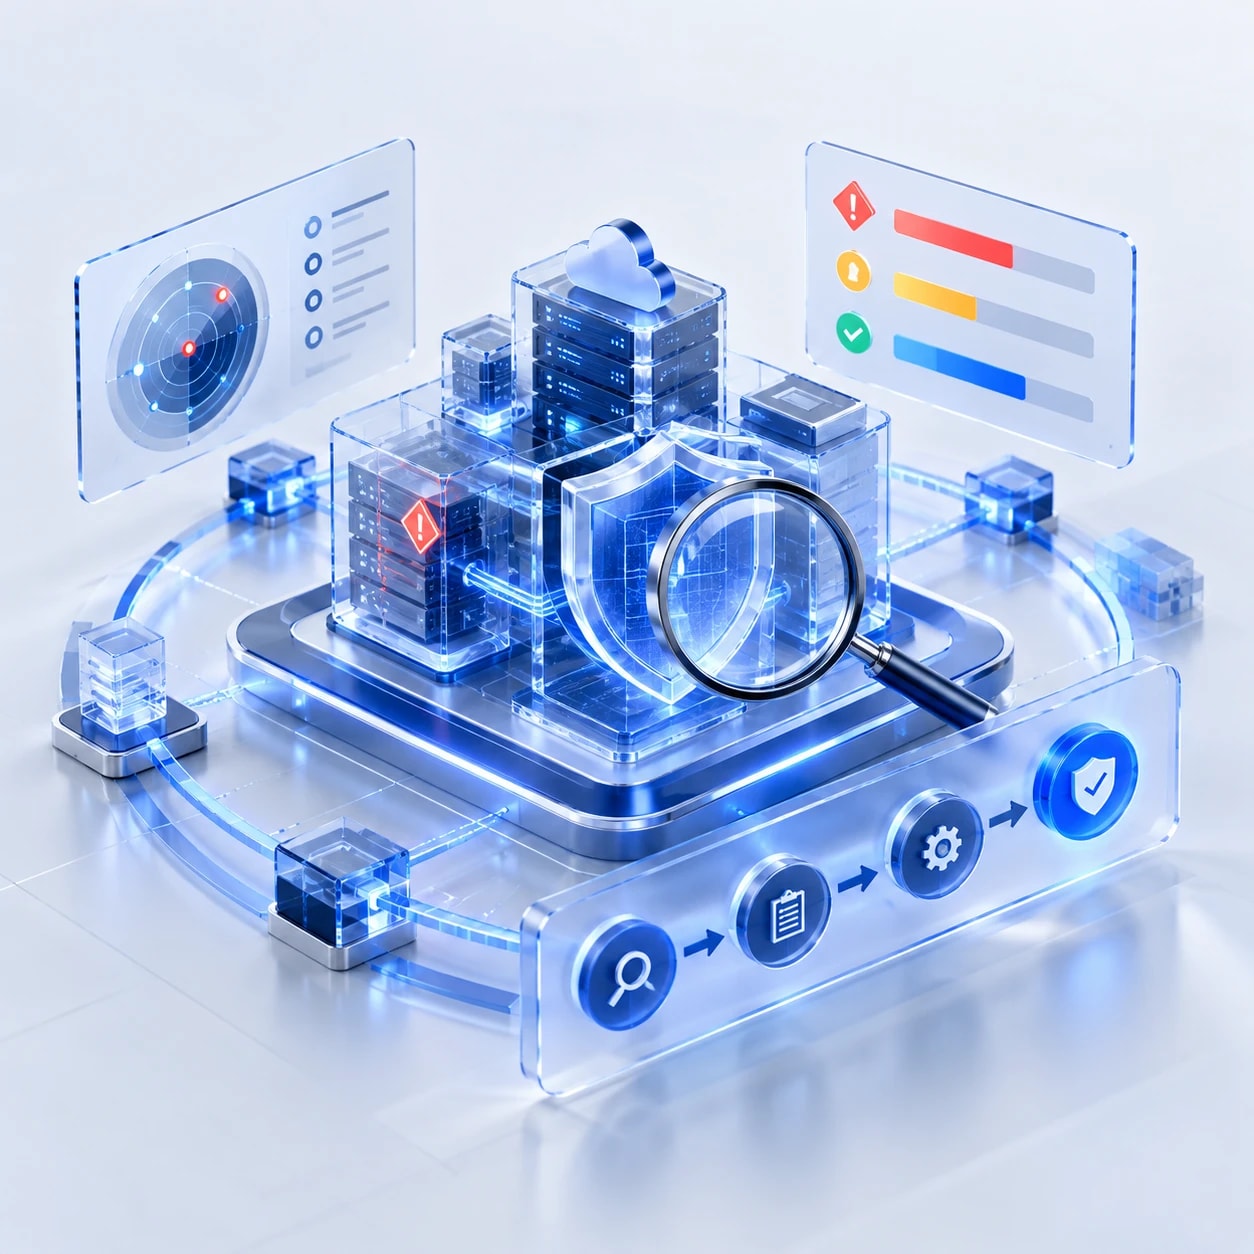
Understand your real security posture and get a prioritized roadmap to close the gaps.
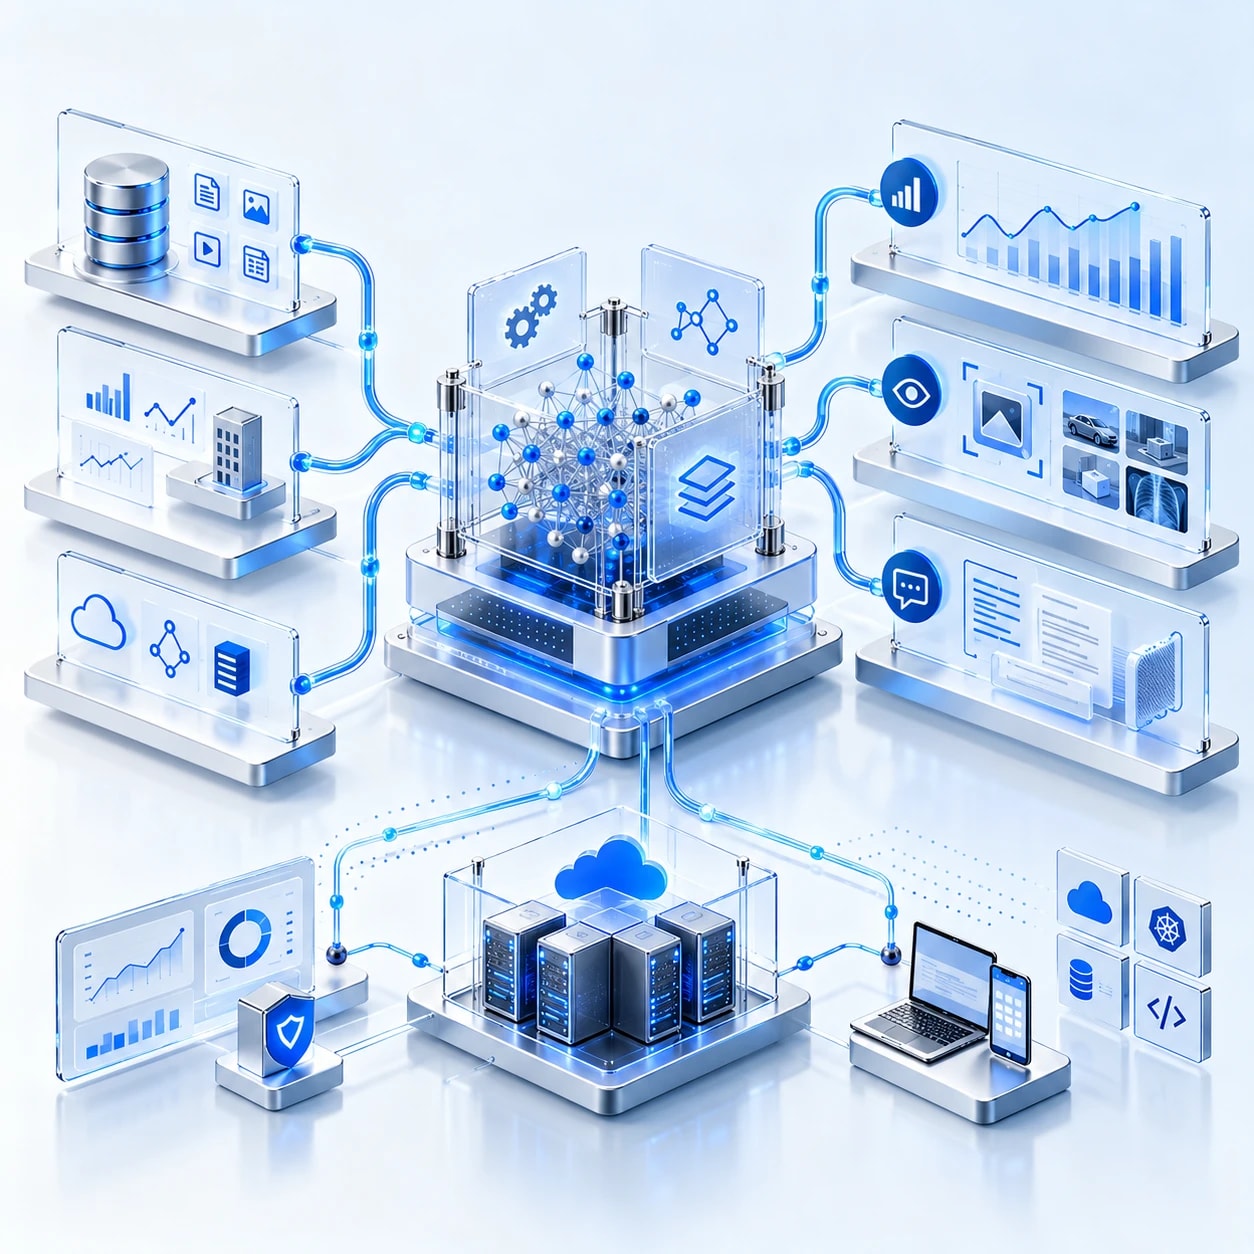
Production AI models built on your own data, running in your operations.
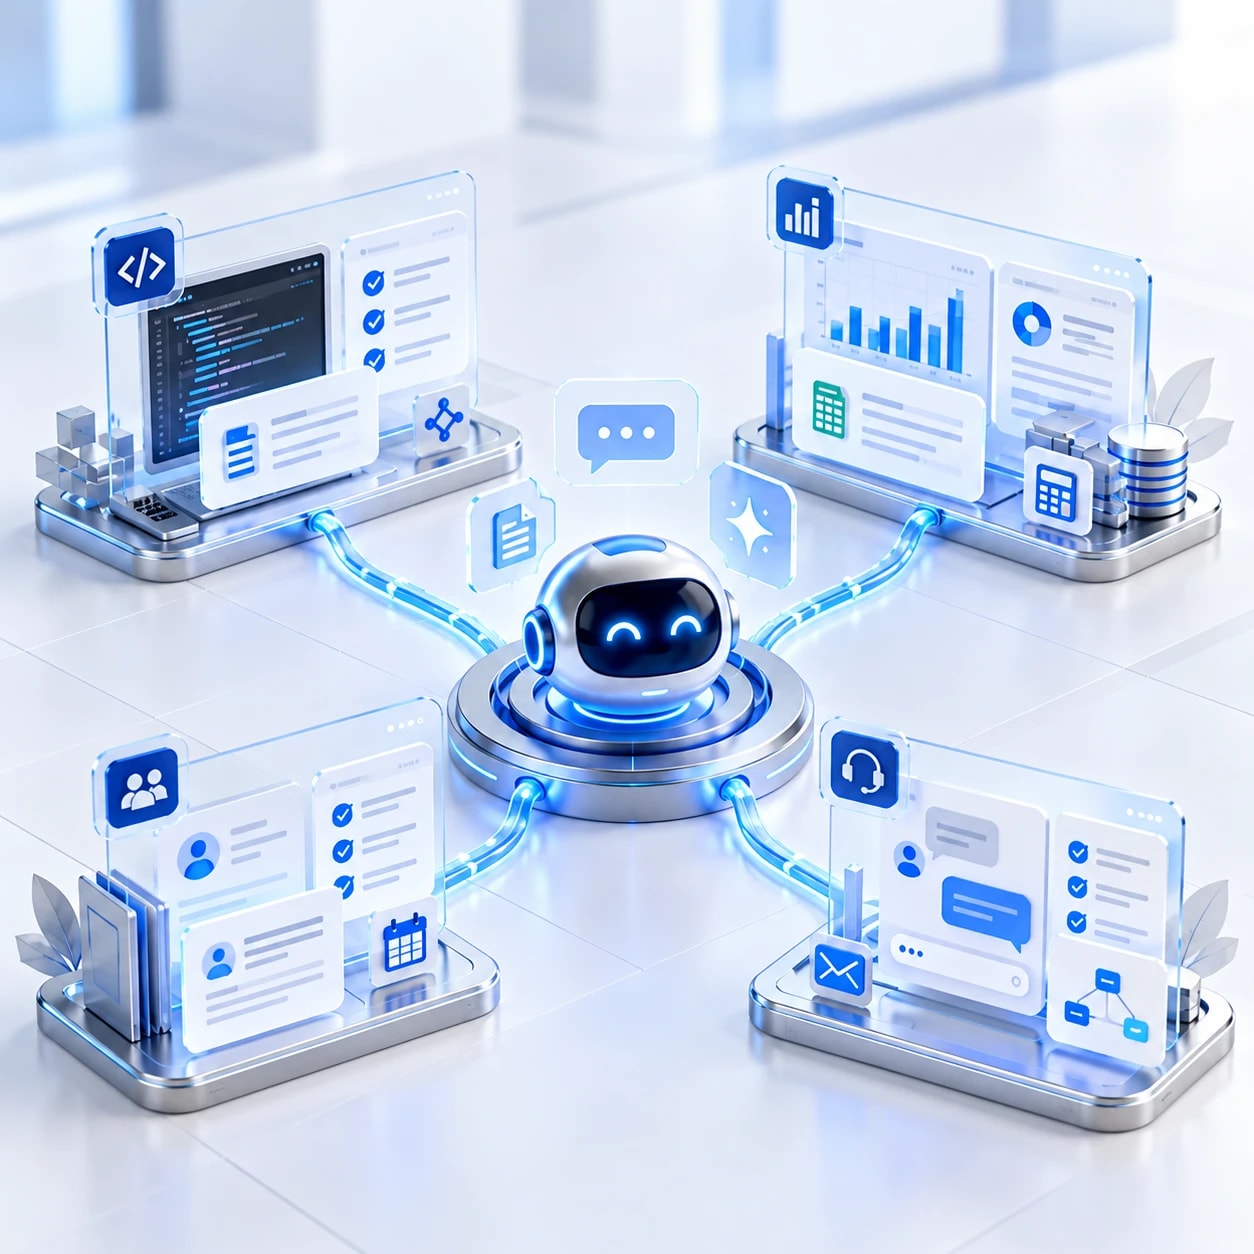
AI copilots, assistants and agents that do real work, with people kept in control.
Start securing your AI so you can deploy it with confidence, not exposure.